
Next up, Beep! The ping is running, the nmap is scanning! Lets have a look at this golden oldy!
Right off the bat, the sV and sC flag makes the scan time out or something. So just a simple nmap scan is what we fall back to.
┌──(root㉿kali)-[/home/kali/htb/knife]
└─# nmap -p- 10.129.229.183
Starting Nmap 7.98 ( https://nmap.org ) at 2026-02-01 11:42 -0500
Nmap scan report for 10.129.229.183
Host is up (0.0070s latency).
Not shown: 65519 closed tcp ports (reset)
PORT      STATE SERVICE
22/tcp    open  ssh
25/tcp    open  smtp
80/tcp    open  http
110/tcp   open  pop3
111/tcp   open  rpcbind
143/tcp   open  imap
443/tcp   open  https
856/tcp   open  unknown
993/tcp   open  imaps
995/tcp   open  pop3s
3306/tcp  open  mysql
4190/tcp  open  sieve
4445/tcp  open  upnotifyp
4559/tcp  open  hylafax
5038/tcp  open  unknown
10000/tcp open  snet-sensor-mgmt
A lot of ports! Going to port 80, it redirects to HTTPS, that seems to not support TLS1.2 or higher. Thats kinda interesting, i mean, its an older box. Perhaps i should try and see if i can get firefox to accept lower TLS versions. Changing the setting in about:config called security.tls.version.min to 1.
We now see the web-page:
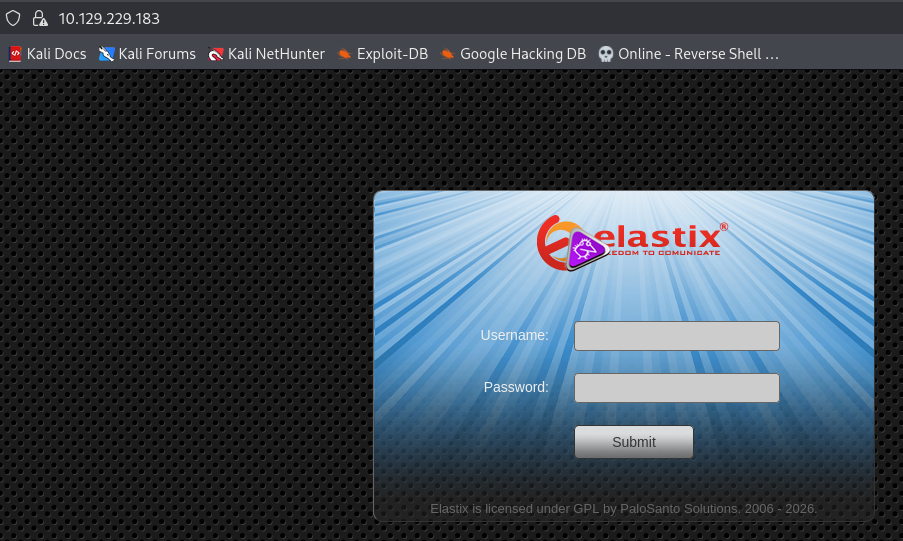
Lets see if elastix has known vulnerabilities. There’s a couple on exploit-db. Lets try out a couple.